If you’re searching how to fix an ex4 file, change vmcode, install an ex5 EA, change the feeder IP or block MT5 updates to keep a crack running — stop. Those steps exist to keep malware alive on your machine. Here’s the safe path.
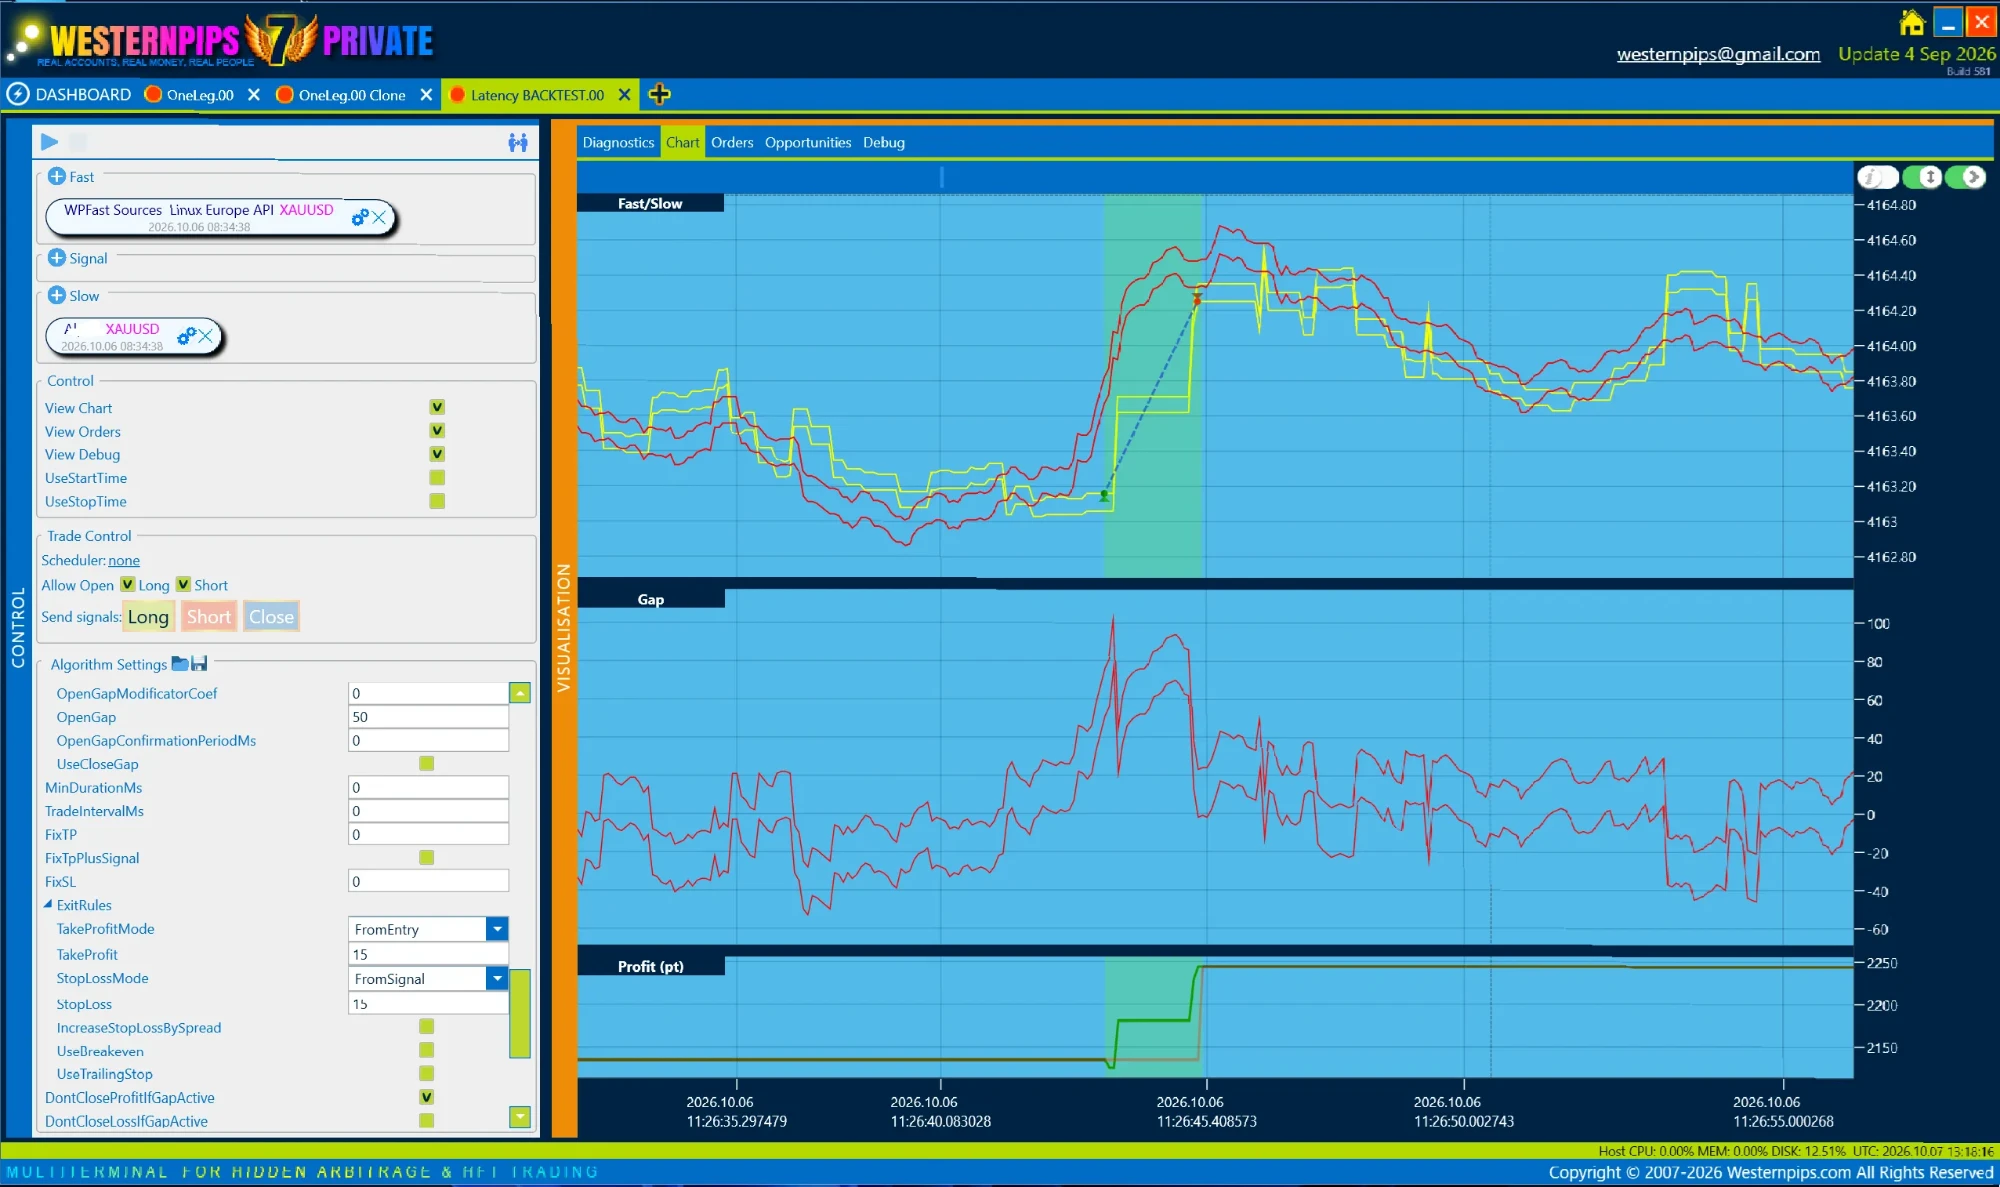 Genuine Westernpips Private 7 — the only real software
Don’t — if you must fix ex4 files, change vmcode, reroute the feeder IP or block MT5 updates to run Westernpips, you are fighting a tampered, malware-laden crack, not using legitimate software. The genuine Westernpips app from Westernpips Private 7 installs and runs without any of these workarounds.
A real product doesn’t need these hacks. Editing ex4/ex5 files, faking vmcodes, rerouting feeder IPs or blocking updates are all signs you’re fighting a tampered build — not using legitimate software.
Editing a protected EA means defeating its protection — exactly what a crack needs, and what malware hides behind.
Loading an unofficial compiled EA runs code you can’t inspect directly inside your terminal.
Rerouting feeds is an attempt to fake a connection the crack can’t legitimately make.
Blocking updates keeps a broken, exploitable setup frozen — and leaves known security holes open.
Don’t edit EAs, reroute feeds or block updates. Those keep a compromised setup alive.
Disconnect, run a full antivirus scan and remove the cracked files and any “patches”.
From a clean device, change passwords, revoke API keys and enable 2FA. Check your broker.
Download the signed, licensed Westernpips from the official site — no hacks required.
If you’re hacking files to launch it, it isn’t the real product. Get the genuine app instead.
People search for “how to run a Westernpips crack” expecting a setup guide. In reality the “instructions” that circulate are a checklist for disabling your own defences, and following them is the whole attack. Here is what a cracked build does on the machine, step by step, so the risk is concrete rather than abstract.
It almost always begins with a demand to turn protection off. “Disable Windows Defender”, “add an exclusion for the folder”, “pause your antivirus”, “allow through SmartScreen” — every one of these exists so the payload cannot be quarantined. A genuine installer never asks for this. The instant you comply, the one thing standing between the file and your accounts is gone.
Next comes execution and persistence. The loader runs with your user rights, often triggers a UAC prompt to gain more, then plants itself to survive a reboot: a scheduled task, a Run key in the registry, or a copy dropped into a startup folder. From that point the program no longer needs the fake “trading” window, which may never even open.
The stolen data is uploaded to a command-and-control server and sometimes resold within hours. By the time an unusual login or withdrawal appears, the compromise is already old news.
If you have run one, treat the device as fully compromised: disconnect it from the network and, from a different clean device, change your email, broker and exchange passwords, revoke active sessions, and move funds only after the machine is wiped or thoroughly cleaned. Then get the genuine, signed Westernpips Private 7, which never asks you to lower your security to install it.